Joplin
Open-source note taking
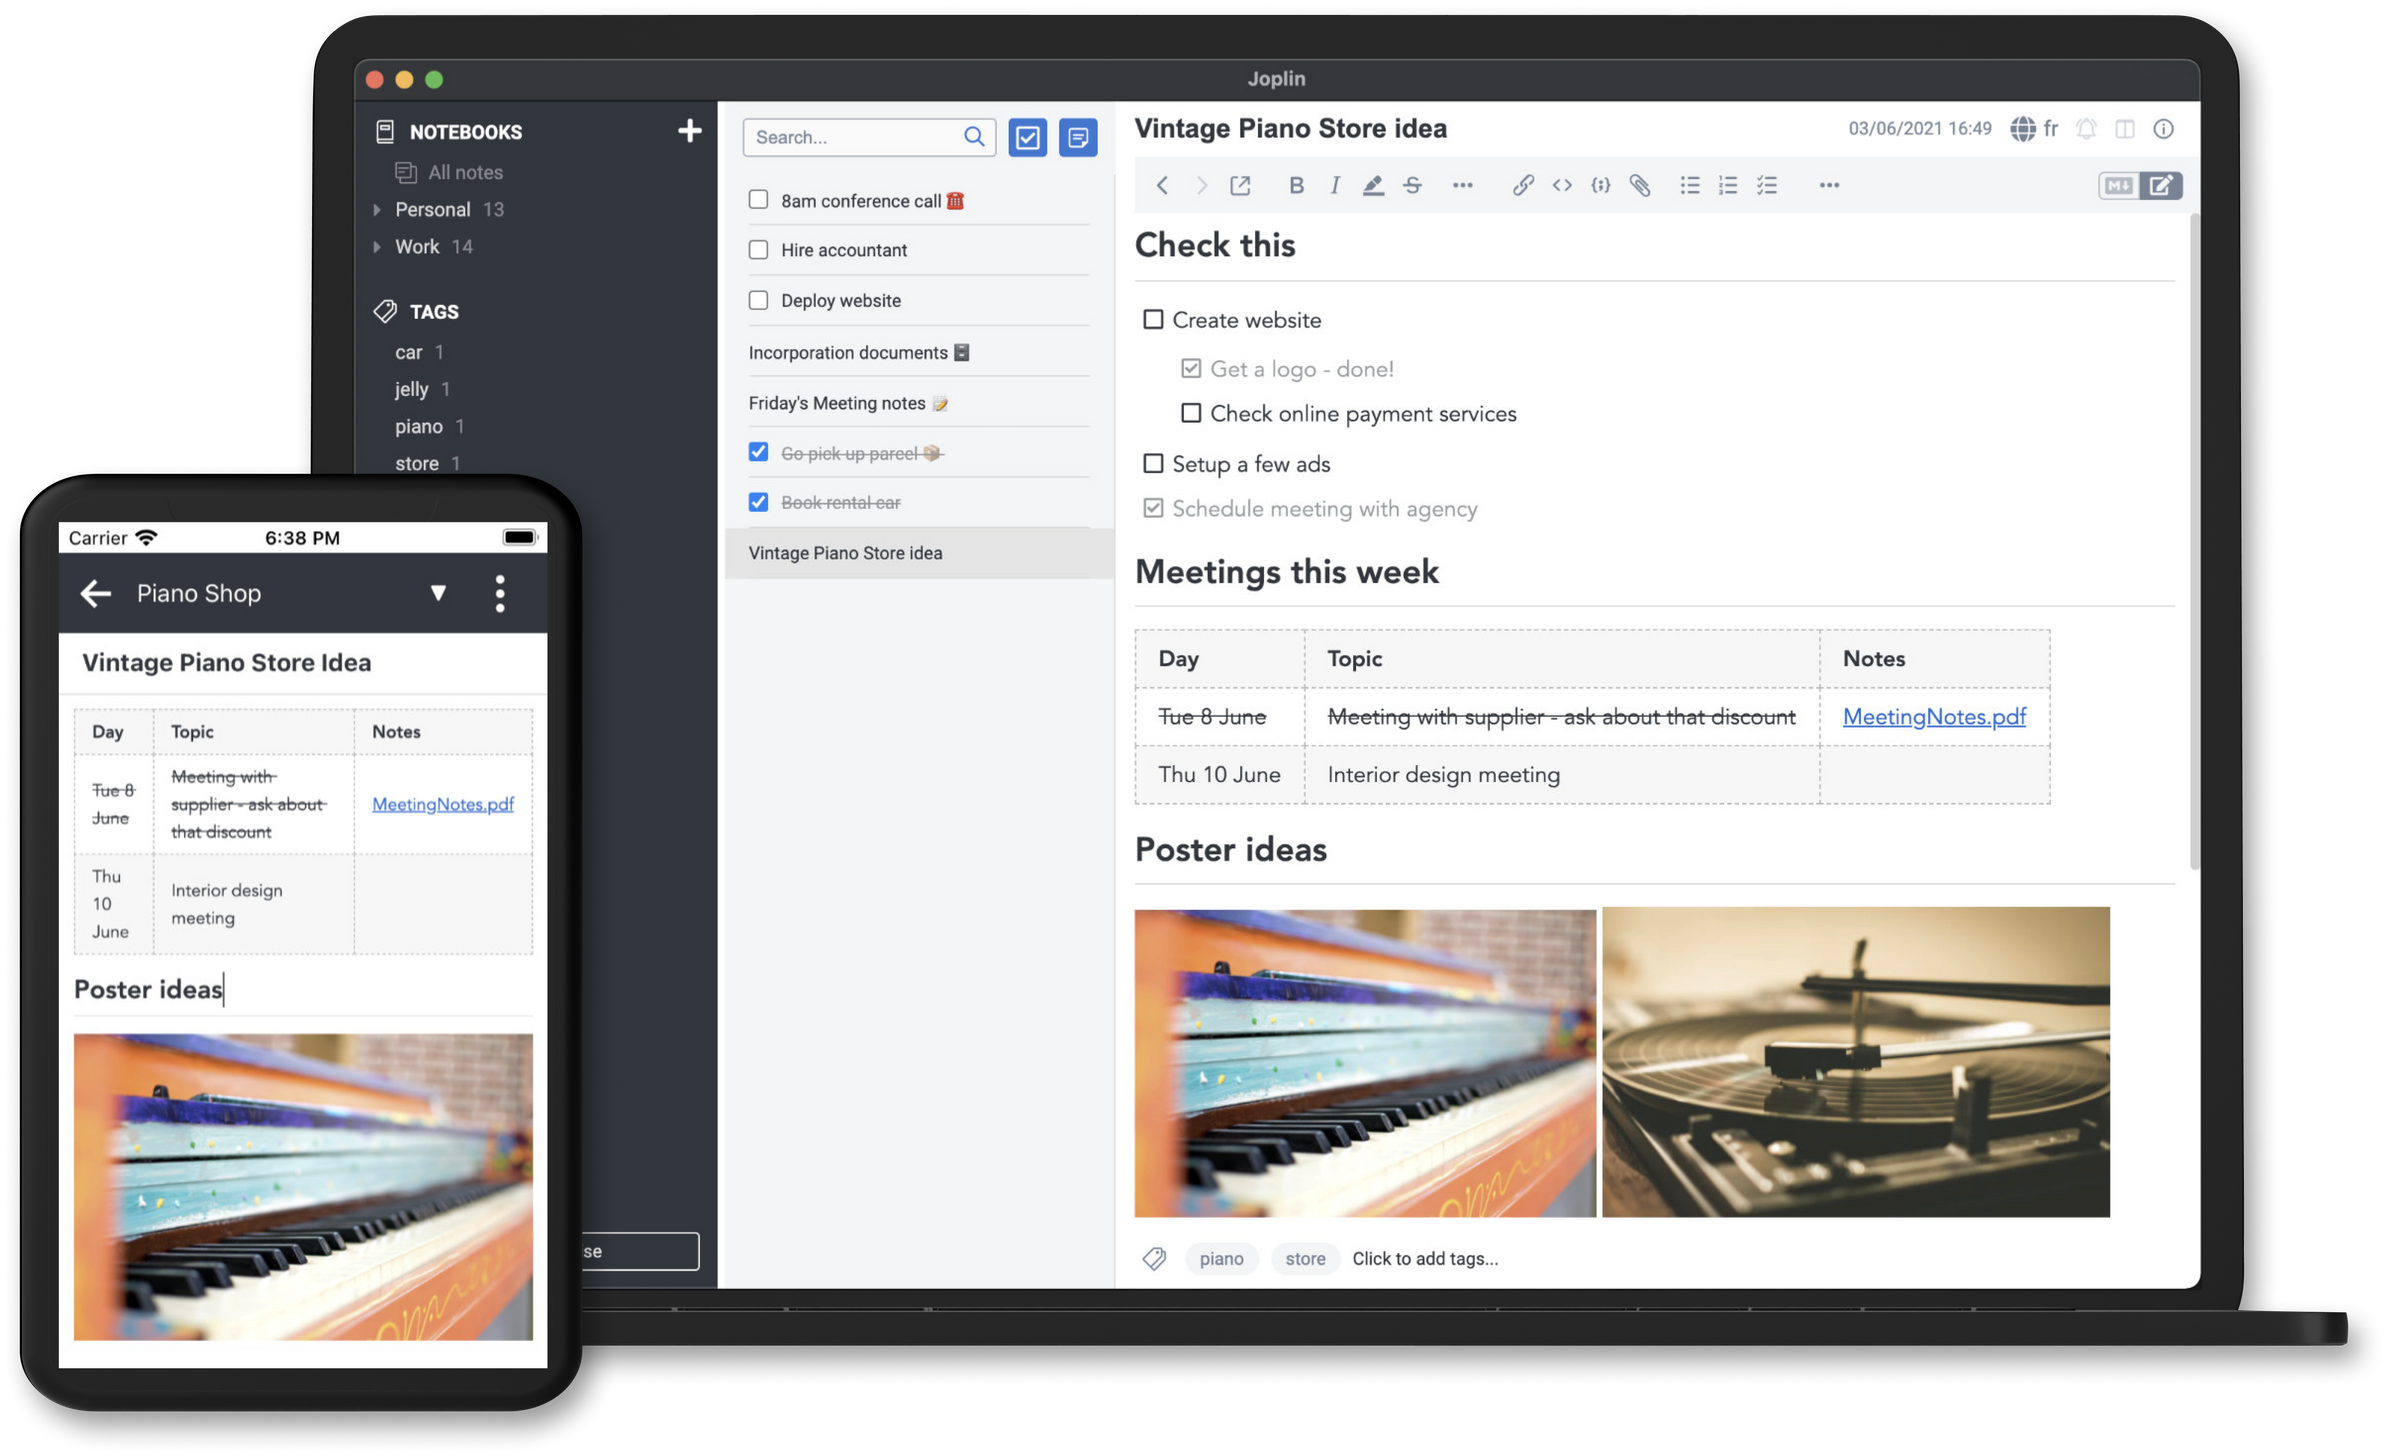
Joplin desktop. This Flatpak wraps the official Linux DEB with zypak. It is not a vendor-official Flatpak.
Joplin is AGPL-3.0; this Flatpak is a redistribution, not vendor official.
Install
flatpak --user remote-add --if-not-exists thepeoples \
  https://flatpak.thepeoples.io/thepeoples.flatpakrepo
flatpak --user install -y thepeoples io.thepeoples.Joplin
flatpak --user install -y thepeoples io.thepeoples.Joplin//3.7.21
Optional system install uses sudo flatpak remote-add --if-not-exists --system and sudo flatpak install -y --system. The //version form pins the advertised ostree branch; stable tracks the latest advertised tree.
Previous versions
The remote keeps the current tree plus the last two vendor versions as extra ostree branches for rollback. Objects stay on the remote after a branch is dropped (publish does not delete).
- Version
3.6.15(ostreeaff0dda63d19267bf765577d330630d71a4ab24b6e01bbcbeec7e9f47920203a)
flatpak --user install -y thepeoples io.thepeoples.Joplin//3.6.15- Version
3.6.16(ostree70329811148c649cc93c5608b521abbff08694189a5e6d3c68285e86a23b7e45)
flatpak --user install -y thepeoples io.thepeoples.Joplin//3.6.16Verify
- App id
io.thepeoples.Joplin, vendor Laurent Cozic, version3.7.21, license AGPL-3.0-or-later - Download 214.0 MB · installed 641.0 MB
- sha256
14de2d5524e45341de5f0b68a1e78191b796a6c9817949c49b80afe5cd6ab965 - Ostree key fingerprint
98D786877B6C4E8C6889CBD2E75B1C5B0CB2D841 - Homepage https://joplinapp.org/
Input scan
Pinned deb Joplin-3.7.21.deb, extracted without install scripts, scanned before wrap. 2026-10-14 19:39 UTC · trivy 0.73.0 · vuln DB 2026-10-14.
Wrap
Layers this remote adds. Gate fails on CRITICAL.
none
gate pass
Vendor
In the upstream package. Not patched here.
7 CRITICAL · 74 HIGH · 36 MEDIUM · 7 LOW
Vendor findings 124 · 7 CRITICAL · 74 HIGH · 36 MEDIUM · 7 LOW
| Severity | ID | Package | Installed | Fixed | Title |
|---|---|---|---|---|---|
| CRITICAL | CVE-2021-44906 | minimist | 1.2.0 | 1.2.6, 0.2.4 | minimist: prototype pollution |
| CRITICAL | CVE-2021-44906 | minimist | 1.2.3 | 1.2.6, 0.2.4 | minimist: prototype pollution |
| CRITICAL | CVE-2023-36665 | protobufjs | 7.2.4 | 7.2.5, 6.11.4 | protobufjs: prototype pollution using user-controlled protobuf message |
| CRITICAL | CVE-2026-41242 | protobufjs | 7.2.4 | 8.0.1, 7.5.5 | protobufjs: protobufjs: Arbitrary code execution via injected protobuf definition type fields |
| CRITICAL | CVE-2026-59873 | tar | 6.0.2 | 7.5.19 | tar: node-tar: Denial of Service via crafted gzip bomb |
| CRITICAL | CVE-2026-59873 | tar | 6.1.11 | 7.5.19 | tar: node-tar: Denial of Service via crafted gzip bomb |
| CRITICAL | CVE-2026-59873 | tar | 6.1.2 | 7.5.19 | tar: node-tar: Denial of Service via crafted gzip bomb |
| HIGH | CVE-2026-102282 | adm-zip | 0.5.16 | 0.6.1 | adm-zip: adm-zip: Privilege escalation via unfiltered permission bits in extracted archives |
| HIGH | CVE-2026-39244 | adm-zip | 0.5.16 | 0.6.0 | adm-zip: adm-zip: Denial of Service via crafted ZIP file leading to excessive memory allocation |
| HIGH | CVE-2026-77301 | adm-zip | 0.5.16 | 0.6.1 | adm-zip: adm-zip: Denial of Service via uncontrolled memory allocation |
| HIGH | GHSA-8238-w5pm-2374 | adm-zip | 0.5.16 | 0.6.1 | adm-zip: Unhandled error event in async DEFLATE decompression crashes Node.js process (DoS) |
| HIGH | GHSA-rcw4-f5rp-g42v | adm-zip | 0.5.16 | 0.6.1 | adm-zip: Decompression-bomb protection (fix for CVE-2026-39244) can be bypassed by declaring uncompressed size as 0 |
| HIGH | CVE-2026-102276 | brace-expansion | 1.1.7 | 5.0.10, 3.0.7, 2.1.5, 1.1.19 | brace-expansion: brace-expansion: Denial of Service via stack exhaustion from crafted brace patterns |
| HIGH | CVE-2026-102278 | brace-expansion | 1.1.7 | 5.0.11, 3.0.8, 2.1.6, 1.1.20 | brace-expansion: brace-expansion: Denial of Service via uncontrolled recursion in nested brace patterns |
| HIGH | CVE-2026-13149 | brace-expansion | 1.1.7 | 5.0.7, 1.1.16, 2.1.2 | brace-expansion: Brace-expansion: Denial of Service due to exponential-time complexity |
| HIGH | CVE-2026-14257 | brace-expansion | 1.1.7 | 5.0.8, 3.0.3, 2.1.3, 1.1.17 | brace-expansion: Brace-expansion: Denial of Service via memory exhaustion in expand() function |
| HIGH | CVE-2026-69152 | brace-expansion | 1.1.7 | 1.1.18, 2.1.4, 3.0.6, 5.0.9 | brace-expansion: DoS via unbounded intermediate arrays, bypassing the CVE-2026-14257 mitigation |
| HIGH | CVE-2026-102673 | electron | 39.8.5 | 41.10.4, 42.5.2, 43.0.0 | electron: Electron: Sandbox bypass via popups opened from sandboxed iframes |
| HIGH | CVE-2026-102674 | electron | 39.8.5 | 41.10.6, 42.9.2, 43.4.1, 44.0.0-beta.5 | electron: Electron: Sandbox bypass via popup window creation |
| HIGH | CVE-2026-102675 | electron | 39.8.5 | 41.10.6, 42.9.2, 43.4.1, 44.0.0-beta.5 | electron: Electron: Cross-origin information disclosure via improper CORS enforcement in custom protocol handlers |
| HIGH | CVE-2026-102676 | electron | 39.8.5 | 41.10.6, 42.9.2, 43.4.1, 44.0.0-beta.5 | electron: electron: Privilege escalation via unauthorized Node.js integration in web workers |
| HIGH | CVE-2026-70601 | electron | 39.8.5 | 39.8.9, 40.9.2, 41.2.2, 42.0.0-beta.5 | Electron: Context isolation bypass via Function.prototype.bind hijack |
| HIGH | CVE-2026-70604 | electron | 39.8.5 | 42.0.0, 41.4.0, 40.9.3, 39.8.10 | Electron: Custom protocol with supportFetchAPI but not corsEnabled allows cross-origin reads |
| HIGH | CVE-2026-70608 | electron | 39.8.5 | 42.0.1, 41.10.3, 39.8.10 | Electron: Sandboxed iframe can bypass the allow-popups restriction via the OpenURL navigation path |
| HIGH | CVE-2022-25881 | http-cache-semantics | 4.1.0 | 4.1.1 | http-cache-semantics: Regular Expression Denial of Service (ReDoS) vulnerability |
| HIGH | CVE-2026-93748 | http-cache-semantics | 4.1.0 | — | http-cache-semantics: http-cache-semantics: Information Disclosure via max-stale directive |
| HIGH | CVE-2020-7788 | ini | 1.3.0 | 1.3.6 | nodejs-ini: Prototype pollution via malicious INI file |
| HIGH | CVE-2024-29415 | ip | 1.1.5 | — | node-ip: Incomplete fix for CVE-2023-42282 |
| HIGH | CVE-2022-3517 | minimatch | 3.0.4 | 3.0.5 | nodejs-minimatch: ReDoS via the braceExpand function |
| HIGH | CVE-2026-26996 | minimatch | 3.0.4 | 10.2.1, 9.0.6, 8.0.5, 7.4.7, 6.2.1, 5.1.7, 4.2.4, 3.1.3 | minimatch: minimatch: Denial of Service via specially crafted glob patterns |
| HIGH | CVE-2026-27903 | minimatch | 3.0.4 | 10.2.3, 9.0.7, 8.0.6, 7.4.8, 6.2.2, 5.1.8, 4.2.5, 3.1.3 | minimatch: minimatch: Denial of Service due to unbounded recursive backtracking via crafted glob patterns |
| HIGH | CVE-2026-27904 | minimatch | 3.0.4 | 10.2.3, 9.0.7, 8.0.6, 7.4.8, 6.2.2, 5.1.8, 4.2.5, 3.1.4 | minimatch: Minimatch: Denial of Service via catastrophic backtracking in glob expressions |
| HIGH | CVE-2026-44289 | protobufjs | 7.2.4 | 7.5.6, 8.0.2 | protobufjs: protobufjs: Denial of Service via uncontrolled recursion in protobuf decoding |
| HIGH | CVE-2026-44290 | protobufjs | 7.2.4 | 7.5.6, 8.0.2 | protobufjs: protobufjs: Denial of Service via crafted schema |
| HIGH | CVE-2026-44291 | protobufjs | 7.2.4 | 7.5.6, 8.0.2 | protobufjs: protobufjs: Arbitrary Code Execution via prototype pollution |
| HIGH | CVE-2026-44293 | protobufjs | 7.2.4 | 7.5.6, 8.0.2 | protobufjs: protobufjs: Arbitrary code execution due to unsafe expression generation from crafted protobuf descriptors |
| HIGH | CVE-2026-48712 | protobufjs | 7.2.4 | 7.6.1, 8.4.1 | protobufjs: protobufjs: Denial of Service via uncontrolled recursion with crafted protobuf payload |
| HIGH | CVE-2022-24713 | regex | 1.4.6 | 1.5.5 | Mozilla: Denial of Service via complex regular expressions |
| HIGH | CVE-2022-25883 | semver | 6.0.0 | 7.5.2, 6.3.1, 5.7.2 | nodejs-semver: Regular expression denial of service |
| HIGH | CVE-2022-25883 | semver | 7.3.2 | 7.5.2, 6.3.1, 5.7.2 | nodejs-semver: Regular expression denial of service |
| HIGH | CVE-2022-25883 | semver | 7.3.5 | 7.5.2, 6.3.1, 5.7.2 | nodejs-semver: Regular expression denial of service |
| HIGH | GHSA-f88m-g3jw-g9cj | sharp | 0.34.5 | 0.35.0 | sharp inherited vulnerabilities in libvips: CVE-2026-33327, CVE-2026-33328, CVE-2026-35590, CVE-2026-35591 |
| HIGH | GHSA-rgj7-g3m4-5g8c | sharp | 0.34.5 | 0.35.4 | sharp: Vulnerabilities in libheif: GHSA-g89c-p67h-r497 and GHSA-2jg2-4ch7-h545 |
| HIGH | GHSA-wq5f-xc86-pv6w | sharp | 0.34.5 | 0.35.5 | sharp : Vulnerability in librsvg dependency CVE-2026-96889 |
| HIGH | CVE-2022-0355 | simple-get | 4.0.0 | 4.0.1, 3.1.1, 2.8.2 | simple-get: exposure of sensitive information to an unauthorized actor |
| HIGH | CVE-2021-27290 | ssri | 8.0.0 | 6.0.2, 7.1.1, 8.0.1 | nodejs-ssri: Regular expression DoS (ReDoS) when parsing malicious SRI in strict mode |
| HIGH | CVE-2021-32803 | tar | 6.0.2 | 3.2.3, 4.4.15, 5.0.7, 6.1.2 | nodejs-tar: Insufficient symlink protection allowing arbitrary file creation and overwrite |
| HIGH | CVE-2021-32804 | tar | 6.0.2 | 3.2.2, 4.4.14, 5.0.6, 6.1.1 | nodejs-tar: Insufficient absolute path sanitization allowing arbitrary file creation and overwrite |
| HIGH | CVE-2021-37701 | tar | 6.0.2 | 4.4.16, 5.0.8, 6.1.7 | nodejs-tar: Insufficient symlink protection due to directory cache poisoning using symbolic links allowing arbitrary file creation and overwrite |
| HIGH | CVE-2021-37701 | tar | 6.1.2 | 4.4.16, 5.0.8, 6.1.7 | nodejs-tar: Insufficient symlink protection due to directory cache poisoning using symbolic links allowing arbitrary file creation and overwrite |
| HIGH | CVE-2021-37712 | tar | 6.0.2 | 4.4.18, 5.0.10, 6.1.9 | nodejs-tar: Insufficient symlink protection due to directory cache poisoning using symbolic links allowing arbitrary file creation and overwrite |
| HIGH | CVE-2021-37712 | tar | 6.1.2 | 4.4.18, 5.0.10, 6.1.9 | nodejs-tar: Insufficient symlink protection due to directory cache poisoning using symbolic links allowing arbitrary file creation and overwrite |
| HIGH | CVE-2021-37713 | tar | 6.0.2 | 4.4.18, 5.0.10, 6.1.9 | nodejs-tar: Arbitrary File Creation/Overwrite on Windows via insufficient relative path sanitization |
| HIGH | CVE-2021-37713 | tar | 6.1.2 | 4.4.18, 5.0.10, 6.1.9 | nodejs-tar: Arbitrary File Creation/Overwrite on Windows via insufficient relative path sanitization |
| HIGH | CVE-2026-23745 | tar | 6.0.2 | 7.5.3 | node-tar: tar: node-tar: Arbitrary file overwrite and symlink poisoning via unsanitized linkpaths in archives |
| HIGH | CVE-2026-23745 | tar | 6.1.11 | 7.5.3 | node-tar: tar: node-tar: Arbitrary file overwrite and symlink poisoning via unsanitized linkpaths in archives |
| HIGH | CVE-2026-23745 | tar | 6.1.2 | 7.5.3 | node-tar: tar: node-tar: Arbitrary file overwrite and symlink poisoning via unsanitized linkpaths in archives |
| HIGH | CVE-2026-23950 | tar | 6.0.2 | 7.5.4 | node-tar: tar: node-tar: Arbitrary file overwrite via Unicode path collision race condition |
| HIGH | CVE-2026-23950 | tar | 6.1.11 | 7.5.4 | node-tar: tar: node-tar: Arbitrary file overwrite via Unicode path collision race condition |
| HIGH | CVE-2026-23950 | tar | 6.1.2 | 7.5.4 | node-tar: tar: node-tar: Arbitrary file overwrite via Unicode path collision race condition |
| HIGH | CVE-2026-24842 | tar | 6.0.2 | 7.5.7 | node-tar: tar: node-tar: Arbitrary file creation via path traversal bypass in hardlink security check |
| HIGH | CVE-2026-24842 | tar | 6.1.11 | 7.5.7 | node-tar: tar: node-tar: Arbitrary file creation via path traversal bypass in hardlink security check |
| HIGH | CVE-2026-24842 | tar | 6.1.2 | 7.5.7 | node-tar: tar: node-tar: Arbitrary file creation via path traversal bypass in hardlink security check |
| HIGH | CVE-2026-26960 | tar | 6.0.2 | 7.5.8 | node-tar: node-tar: Arbitrary file read/write via malicious archive hardlink creation |
| HIGH | CVE-2026-26960 | tar | 6.1.11 | 7.5.8 | node-tar: node-tar: Arbitrary file read/write via malicious archive hardlink creation |
| HIGH | CVE-2026-26960 | tar | 6.1.2 | 7.5.8 | node-tar: node-tar: Arbitrary file read/write via malicious archive hardlink creation |
| HIGH | CVE-2026-29786 | tar | 6.0.2 | 7.5.10 | node-tar: hardlink path traversal via drive-relative linkpath |
| HIGH | CVE-2026-29786 | tar | 6.1.11 | 7.5.10 | node-tar: hardlink path traversal via drive-relative linkpath |
| HIGH | CVE-2026-29786 | tar | 6.1.2 | 7.5.10 | node-tar: hardlink path traversal via drive-relative linkpath |
| HIGH | CVE-2026-31802 | tar | 6.0.2 | 7.5.11 | tar: tar: File overwrite via drive-relative symlink traversal |
| HIGH | CVE-2026-31802 | tar | 6.1.11 | 7.5.11 | tar: tar: File overwrite via drive-relative symlink traversal |
| HIGH | CVE-2026-31802 | tar | 6.1.2 | 7.5.11 | tar: tar: File overwrite via drive-relative symlink traversal |
| HIGH | CVE-2026-59874 | tar | 6.0.2 | 7.5.18 | tar: Node-tar: Denial of Service via malformed tar archive header |
| HIGH | CVE-2026-59874 | tar | 6.1.11 | 7.5.18 | tar: Node-tar: Denial of Service via malformed tar archive header |
| HIGH | CVE-2026-59874 | tar | 6.1.2 | 7.5.18 | tar: Node-tar: Denial of Service via malformed tar archive header |
| HIGH | CVE-2026-73566 | tar | 6.0.2 | 7.5.21 | tar: node-tar: Denial of Service via crafted long-path tar archive |
| HIGH | CVE-2026-73566 | tar | 6.1.11 | 7.5.21 | tar: node-tar: Denial of Service via crafted long-path tar archive |
| HIGH | CVE-2026-73566 | tar | 6.1.2 | 7.5.21 | tar: node-tar: Denial of Service via crafted long-path tar archive |
| HIGH | CVE-2024-12905 | tar-fs | 2.0.0 | 1.16.4, 2.1.2, 3.0.7 | tar-fs: link following and path traversal via maliciously crafted tar file |
| HIGH | CVE-2025-48387 | tar-fs | 2.0.0 | 1.16.5, 2.1.3, 3.0.9 | tar-fs: tar-fs has issue where extract can write outside the specified dir with a specific tarball |
| HIGH | CVE-2025-59343 | tar-fs | 2.0.0 | 3.1.1, 2.1.4, 1.16.6 | tar-fs: tar-fs symlink validation bypass |
| MEDIUM | CVE-2026-76845 | adm-zip | 0.5.16 | — | adm-zip: adm-zip: Arbitrary File Overwrite via Symlink Following |
| MEDIUM | GHSA-c6fg-446q-cg94 | adm-zip | 0.5.16 | 0.6.1 | adm-zip: getDataAsync() bypasses the maxOutputLength size guard enforced by the synchronous getData() path |
| MEDIUM | GHSA-p634-w6r4-rjp2 | adm-zip | 0.5.16 | 0.6.1 | adm-zip: Duplicate ZIP entry names: getEntry() and extractAllTo() resolve to different content |
| MEDIUM | CVE-2026-102277 | brace-expansion | 1.1.7 | 5.0.12, 3.0.9, 2.1.7, 1.1.21 | brace-expansion: brace-expansion: Denial of Service via crafted brace patterns |
| MEDIUM | CVE-2026-33750 | brace-expansion | 1.1.7 | 5.0.5, 3.0.2, 2.0.3, 1.1.13 | brace-expansion: brace-expansion: Denial of Service via zero step value in brace pattern |
| MEDIUM | CVE-2026-25541 | bytes | 1.10.1 | 1.11.1 | Bytes is a utility library for working with bytes. From version 1.2.1 ... |
| MEDIUM | CVE-2026-102672 | electron | 39.8.5 | 39.8.10, 41.10.5, 42.0.0-beta.2 | Electron: Local race condition in Squirrel.Mac update installation on macOS |
| MEDIUM | CVE-2026-70597 | electron | 39.8.5 | 39.8.8, 40.9.1, 41.2.1, 42.0.0-beta.3 | Electron: Parent process code-sign check is spoofable |
| MEDIUM | CVE-2026-70599 | electron | 39.8.5 | 39.8.7, 40.9.0, 41.2.0, 42.0.0-beta.1 | Electron: Permission Check Handler Receives Main Frame Origin Instead of Requesting Iframe Origin |
| MEDIUM | CVE-2026-70602 | electron | 39.8.5 | 39.8.8, 40.9.0, 41.2.1, 42.0.0-beta.3 | Electron: Extension tab APIs operate across session boundaries |
| MEDIUM | CVE-2026-70603 | electron | 39.8.5 | 42.0.0-beta.1, 41.1.1, 40.9.0, 39.8.6 | Electron: shell.openPath path validation bypass via embedded null byte |
| MEDIUM | CVE-2026-70605 | electron | 39.8.5 | 39.8.8, 40.9.1, 41.2.1, 42.0.0-beta.3 | Electron: HTTP redirect followed into local file loader |
| MEDIUM | CVE-2026-70607 | electron | 39.8.5 | 39.8.8, 40.9.0, 41.2.1, 42.0.0-beta.3 | Electron: window.open features string controls some window options considered privileged |
| MEDIUM | CVE-2026-70609 | electron | 39.8.5 | 39.8.7, 40.9.0, 41.2.0, 42.0.0-beta.1 | Electron: DevTools JavaScript Injection via Unsanitized Dock State Parameter |
| MEDIUM | CVE-2026-70610 | electron | 39.8.5 | 39.8.9, 40.9.2, 41.2.2, 42.0.0-beta.4 | Electron: contextBridge object copy honors prototype setters |
| MEDIUM | CVE-2026-70611 | electron | 39.8.5 | 39.8.9, 40.9.2, 41.2.1, 42.0.0-beta.3 | Electron: DevTools embedder handler executes arbitrary files via shell open |
| MEDIUM | CVE-2026-70612 | electron | 39.8.5 | 39.8.8, 40.9.0, 41.2.1, 42.0.0-beta.3 | Electron: Sandboxed iframes can launch external protocol handlers |
| MEDIUM | CVE-2020-7598 | minimist | 1.2.0 | 0.2.1, 1.2.3 | nodejs-minimist: prototype pollution allows adding or modifying properties of Object.prototype using a constructor or __proto__ payload |
| MEDIUM | CVE-2026-44288 | protobufjs | 7.2.4 | 7.5.6, 8.0.2 | protobufjs: protobufjs: Security control bypass due to improper handling of overlong UTF-8 sequences |
| MEDIUM | CVE-2026-44292 | protobufjs | 7.2.4 | 7.5.6, 8.0.2 | protobufjs: protobufjs: Data integrity impact due to prototype pollution |
| MEDIUM | CVE-2026-44294 | protobufjs | 7.2.4 | 7.5.6, 8.0.2 | protobufjs: protobufjs: Denial of Service due to unescaped control characters in field names |
| MEDIUM | CVE-2026-45740 | protobufjs | 7.2.4 | 7.5.8, 8.2.0 | protobufjs: protobufjs: Denial of Service via crafted JSON descriptors |
| MEDIUM | CVE-2026-54269 | protobufjs | 7.2.4 | 7.6.3, 8.6.0 | protobufjs: protobufjs-cli: protobufjs: Denial of Service due to name collision with runtime helpers |
| MEDIUM | CVE-2024-28863 | tar | 6.0.2 | 6.2.1 | node-tar: denial of service while parsing a tar file due to lack of folders depth validation |
| MEDIUM | CVE-2024-28863 | tar | 6.1.11 | 6.2.1 | node-tar: denial of service while parsing a tar file due to lack of folders depth validation |
| MEDIUM | CVE-2024-28863 | tar | 6.1.2 | 6.2.1 | node-tar: denial of service while parsing a tar file due to lack of folders depth validation |
| MEDIUM | CVE-2026-53655 | tar | 6.0.2 | 7.5.16 | node-tar: node-tar: File smuggling due to inconsistent tar archive parsing |
| MEDIUM | CVE-2026-53655 | tar | 6.1.11 | 7.5.16 | node-tar: node-tar: File smuggling due to inconsistent tar archive parsing |
| MEDIUM | CVE-2026-53655 | tar | 6.1.2 | 7.5.16 | node-tar: node-tar: File smuggling due to inconsistent tar archive parsing |
| MEDIUM | CVE-2026-59871 | tar | 6.0.2 | 7.5.18 | node-tar: node-tar: Denial of Service due to incorrect PAX path handling |
| MEDIUM | CVE-2026-59871 | tar | 6.1.11 | 7.5.18 | node-tar: node-tar: Denial of Service due to incorrect PAX path handling |
| MEDIUM | CVE-2026-59871 | tar | 6.1.2 | 7.5.18 | node-tar: node-tar: Denial of Service due to incorrect PAX path handling |
| MEDIUM | CVE-2026-59875 | tar | 6.0.2 | 7.5.17 | node-tar: node-tar: Denial of Service via crafted archive with NUL bytes in metadata |
| MEDIUM | CVE-2026-59875 | tar | 6.1.11 | 7.5.17 | node-tar: node-tar: Denial of Service via crafted archive with NUL bytes in metadata |
| MEDIUM | CVE-2026-59875 | tar | 6.1.2 | 7.5.17 | node-tar: node-tar: Denial of Service via crafted archive with NUL bytes in metadata |
| MEDIUM | CVE-2026-25727 | time | 0.3.44 | 0.3.47 | time: time affected by a stack exhaustion denial of service attack |
| LOW | CVE-2025-5889 | brace-expansion | 1.1.7 | 2.0.2, 1.1.12, 3.0.1, 4.0.1 | brace-expansion: juliangruber brace-expansion index.js expand redos |
| LOW | CVE-2017-16137 | debug | 4.1.0 | 2.6.9, 3.1.0, 3.2.7, 4.3.1 | nodejs-debug: Regular expression Denial of Service |
| LOW | CVE-2026-70598 | electron | 39.8.5 | 39.8.10, 40.9.0, 41.2.1, 42.0.0-beta.3 | Electron: Off-screen rendering trusts GPU-supplied geometry over shared-memory size |
| LOW | CVE-2026-70600 | electron | 39.8.5 | 39.8.8, 40.9.1, 41.2.1, 42.0.0-beta.3 | Electron: Cross-origin iframe can position native autofill popup |
| LOW | CVE-2023-42282 | ip | 1.1.5 | 2.0.1, 1.1.9 | nodejs-ip: arbitrary code execution via the isPublic() function |
| LOW | GHSA-cq8v-f236-94qc | rand | 0.7.3 | 0.9.3, 0.10.1, 0.8.6 | Rand is unsound with a custom logger using rand::rng() |
| LOW | CVE-2025-58160 | tracing-subscriber | 0.2.25 | 0.3.20 | tracing-subscriber: Tracing log pollution |
Previous scans
Daily Trivy refresh. Current report plus the last 14 full scans; older copies are deleted.
| Scanned | Vuln DB | Version | Wrap | Vendor | Report |
|---|---|---|---|---|---|
| 2026-10-14 06:51 UTC | 2026-10-14 | 3.7.21 | none | 7 CRITICAL · 74 HIGH · 36 MEDIUM · 7 LOW | JSON |
| 2026-10-13 06:57 UTC | 2026-10-13 | 3.7.21 | none | 7 CRITICAL · 74 HIGH · 36 MEDIUM · 7 LOW | JSON |
| 2026-10-12 09:28 UTC | 2026-10-12 | 3.7.21 | none | 7 CRITICAL · 74 HIGH · 37 MEDIUM · 7 LOW | JSON |
| 2026-10-12 06:51 UTC | 2026-10-12 | 3.7.21 | none | 7 CRITICAL · 74 HIGH · 37 MEDIUM · 7 LOW | JSON |
| 2026-10-11 06:52 UTC | 2026-10-11 | 3.7.21 | none | 7 CRITICAL · 74 HIGH · 37 MEDIUM · 7 LOW | JSON |
| 2026-10-10 06:52 UTC | 2026-10-10 | 3.7.21 | none | 7 CRITICAL · 74 HIGH · 37 MEDIUM · 7 LOW | JSON |
| 2026-10-09 06:51 UTC | 2026-10-08 | 3.7.21 | none | 7 CRITICAL · 74 HIGH · 37 MEDIUM · 7 LOW | JSON |
| 2026-10-08 19:32 UTC | 2026-10-08 | 3.7.21 | none | 7 CRITICAL · 74 HIGH · 37 MEDIUM · 7 LOW | JSON |
| 2026-10-08 06:51 UTC | 2026-10-07 | 3.7.21 | none | 7 CRITICAL · 74 HIGH · 37 MEDIUM · 7 LOW | JSON |
| 2026-10-07 06:51 UTC | 2026-10-07 | 3.7.21 | none | 7 CRITICAL · 74 HIGH · 37 MEDIUM · 7 LOW | JSON |
| 2026-10-06 06:51 UTC | 2026-10-06 | 3.7.21 | none | 7 CRITICAL · 73 HIGH · 37 MEDIUM · 7 LOW | JSON |
| 2026-09-27 07:34 UTC | 2026-09-27 | 3.7.21 | none | 7 CRITICAL · 63 HIGH · 32 MEDIUM · 7 LOW | JSON |
| 2026-09-27 06:52 UTC | 2026-09-27 | 3.7.18 | none | 7 CRITICAL · 63 HIGH · 32 MEDIUM · 7 LOW | JSON |
| 2026-09-26 07:08 UTC | 2026-09-26 | 3.7.18 | none | 7 CRITICAL · 63 HIGH · 32 MEDIUM · 7 LOW | JSON |