Sparrow
Bitcoin wallet with hardware-wallet support
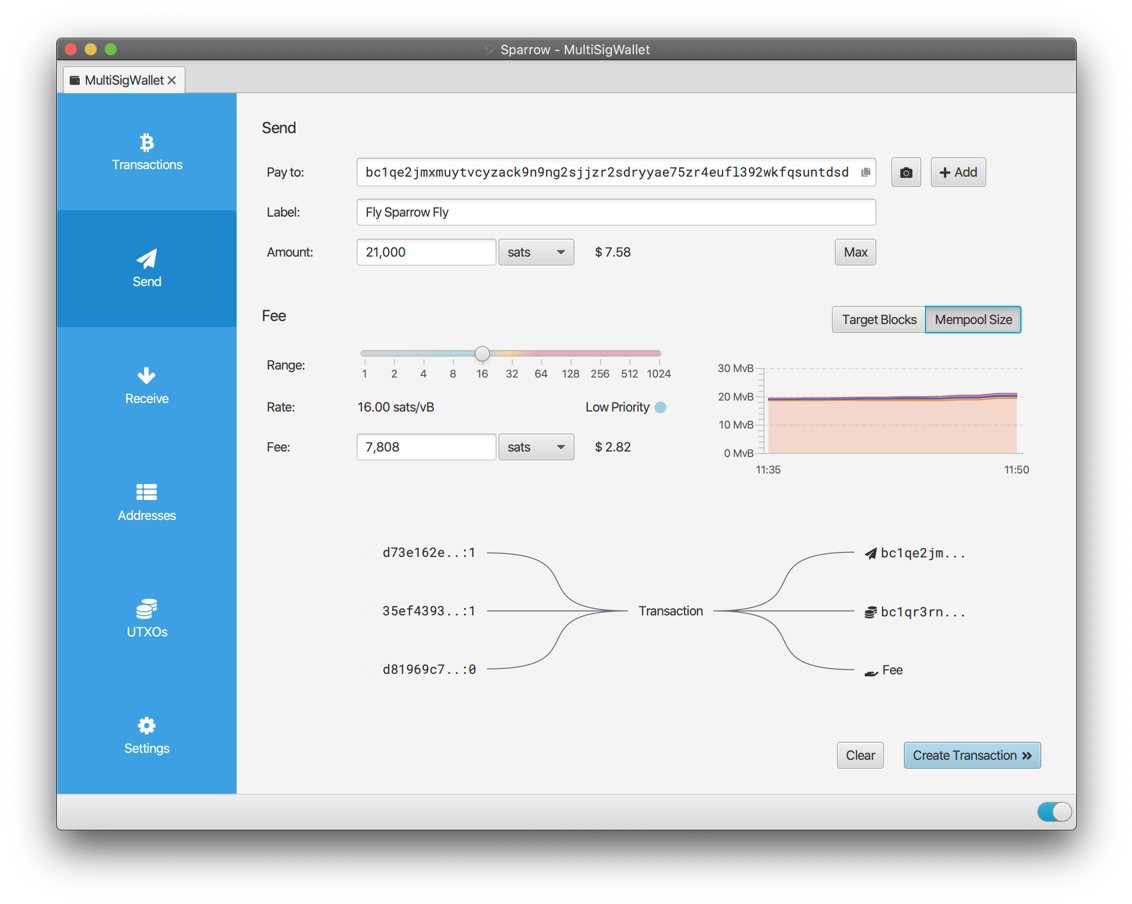
Sparrow is a desktop Bitcoin wallet focused on privacy, hardware wallets, and full verification. This Flatpak wraps the vendor-signed Linux tarball.
Sparrow is Apache-2.0; this Flatpak is a redistribution, not vendor official.
Install
flatpak --user remote-add --if-not-exists thepeoples \
  https://flatpak.thepeoples.io/thepeoples.flatpakrepo
flatpak --user install -y thepeoples io.thepeoples.Sparrow
flatpak --user install -y thepeoples io.thepeoples.Sparrow//2.5.5
Optional system install uses sudo flatpak remote-add --if-not-exists --system and sudo flatpak install -y --system. The //version form pins the advertised ostree branch; stable tracks the latest advertised tree.
Previous versions
The remote keeps the current tree plus the last two vendor versions as extra ostree branches for rollback. Objects stay on the remote after a branch is dropped (publish does not delete).
- Version
2.5.2(ostreebcf6d1c648c98e6524e48143ff3b247c8b524441fe5419aed2c08909a4debbfe)
flatpak --user install -y thepeoples io.thepeoples.Sparrow//2.5.2- Version
2.5.4(ostree1723e8f06ae3a0beea3cc0ae06ba41948bed5c9aed4fb7c62f666edb70dea5d9)
flatpak --user install -y thepeoples io.thepeoples.Sparrow//2.5.4Hardware-wallet udev
The Flatpak cannot write host udev rules. After you install the app, run the helper that ships inside it. It vendor-verifies the same pinned tarball, rewrites rules to uaccess only, and installs them under /etc/udev/rules.d/. It does not add a plugdev group. It will ask for sudo.
sudo ~/.local/share/flatpak/app/io.thepeoples.Sparrow/current/active/files/bin/sparrow-udevSystem install uses the same file under /var/lib/flatpak/app/io.thepeoples.Sparrow/current/active/files/bin/sparrow-udev. Read the script first at /flatpak/helpers/io.thepeoples.Sparrow.sh (sha256 f3c607a3905e334cb0498a250c70a75f7c7b320f12fdc8c9a068fed58f66dc03).
Verify
- App id
io.thepeoples.Sparrow, vendor Sparrow Wallet, version2.5.5, license Apache-2.0 - Download 99.3 MB · installed 130.1 MB
- sha256
7e8a59bf7e7293bd924518dda8ea7747696634297de54878c1c5f5cdb528559d - Ostree key fingerprint
98D786877B6C4E8C6889CBD2E75B1C5B0CB2D841 - Vendor key fingerprint
D4D0D3202FC06849A257B38DE94618334C674B40 - Helper
scripts/post-install/io.thepeoples.Sparrow.shsha256f3c607a3905e334cb0498a250c70a75f7c7b320f12fdc8c9a068fed58f66dc03 - Homepage https://sparrowwallet.com/
Input scan
Pinned tarball sparrowwallet-2.5.5-x86_64.tar.gz, extracted without install scripts, scanned before wrap. 2026-10-14 19:38 UTC · trivy 0.73.0 · vuln DB 2026-10-14.
Wrap
Layers this remote adds. Gate fails on CRITICAL.
none
gate pass
Vendor
In the upstream package. Not patched here.
9 HIGH · 12 MEDIUM · 3 LOW
Vendor findings 24 · 9 HIGH · 12 MEDIUM · 3 LOW
| Severity | ID | Package | Installed | Fixed | Title |
|---|---|---|---|---|---|
| HIGH | CVE-2026-68494 | com.fasterxml.jackson.core:jackson-core | 2.21.1 | 2.18.8, 2.21.4 | com.fasterxml.jackson.core/jackson-core: tools.jackson.core/jackson-core: jackson-core: Denial of Service via incomplete fix in async JSON parser |
| HIGH | CVE-2026-89407 | com.fasterxml.jackson.core:jackson-core | 2.21.1 | 2.18.11, 2.21.7, 2.22.3 | com.fasterxml.jackson/jackson-core: tools.jackson.core/jackson-core: Jackson-core: Denial of Service via regular expression backtracking |
| HIGH | CVE-2026-89425 | com.fasterxml.jackson.core:jackson-core | 2.21.1 | 2.21.7, 2.22.3, 2.18.11 | com.fasterxml.jackson.core/jackson-core: Jackson-core: Denial of Service via unbounded StringBuilder growth during malformed token processing |
| HIGH | CVE-2026-54512 | com.fasterxml.jackson.core:jackson-databind | 2.21.1 | 2.18.8, 3.1.4, 2.21.4 | jackson-databind: jackson-databind: Arbitrary code execution via PolymorphicTypeValidator bypass |
| HIGH | CVE-2026-54513 | com.fasterxml.jackson.core:jackson-databind | 2.21.1 | 2.18.8, 2.21.4, 3.1.4 | jackson-databind: Jackson-databind: Security bypass allows arbitrary code execution |
| HIGH | CVE-2026-68497 | com.fasterxml.jackson.core:jackson-databind | 2.21.1 | 2.18.10, 2.21.6, 2.22.2 | com.fasterxml.jackson.core/jackson-databind: tools.jackson.core/jackson-databind: jackson-databind: CPU Denial of Service via unbounded numeric parsing |
| HIGH | CVE-2026-91776 | com.fasterxml.jackson.core:jackson-databind | 2.21.1 | 2.18.11, 2.21.7, 2.22.3 | jackson-databind: com.fasterxml.jackson/jackson-core: jackson-databind: Denial of Service via unbounded cache growth in TypeDeserializerBase |
| HIGH | CVE-2026-91777 | com.fasterxml.jackson.core:jackson-databind | 2.21.1 | 2.21.7, 2.18.11, 2.22.3 | com.fasterxml.jackson.core/jackson-databind: tools.jackson.core:jackson-databind: Jackson-databind: Denial of Service via quadratic forward-reference completion |
| HIGH | CVE-2026-2332 | org.eclipse.jetty:jetty-http | 9.4.54.v20240208 | 12.1.7, 12.0.33, 11.0.29, 10.0.28, 9.4.60 | org.eclipse.jetty/jetty-http: HTTP request smuggling via chunked extension quoted-string parsing |
| MEDIUM | CVE-2026-19032 | com.fasterxml.jackson.core:jackson-databind | 2.21.1 | 2.18.10, 2.21.6, 2.22.2 | com.fasterxml.jackson.core/jackson-databind: tools.jackson.core/jackson-databind: Jackson-databind: Uncontrolled URI scheme resolution in Path deserialization |
| MEDIUM | CVE-2026-54514 | com.fasterxml.jackson.core:jackson-databind | 2.21.1 | 2.18.8, 2.21.4, 3.1.4 | jackson-databind: jackson-databind: Information Disclosure via Eager DNS Resolution |
| MEDIUM | CVE-2026-54515 | com.fasterxml.jackson.core:jackson-databind | 2.21.1 | 3.1.4, 2.18.9, 2.21.5, 2.22.1 | jackson-databind: jackson-databind: Ignored properties can be unexpectedly modified |
| MEDIUM | CVE-2026-54516 | com.fasterxml.jackson.core:jackson-databind | 2.21.1 | 2.21.4, 3.1.4 | jackson-databind: jackson-databind: Security bypass due to improper handling of renamed properties |
| MEDIUM | CVE-2026-54517 | com.fasterxml.jackson.core:jackson-databind | 2.21.1 | 2.21.4, 3.1.4 | jackson-databind: jackson-databind: Information disclosure via improper JsonView filter application |
| MEDIUM | CVE-2026-54518 | com.fasterxml.jackson.core:jackson-databind | 2.21.1 | 2.21.4 | jackson-databind: jackson-databind: Information disclosure and data manipulation via view-based access control bypass |
| MEDIUM | CVE-2026-59888 | com.fasterxml.jackson.core:jackson-databind | 2.21.1 | 2.18.8, 2.21.4 | com.fasterxml.jackson.core/jackson-databind: tools.jackson.core/jackson-databind: jackson-databind: @JsonIgnore bypass in Java Records |
| MEDIUM | CVE-2026-59889 | com.fasterxml.jackson.core:jackson-databind | 2.21.1 | 2.21.5, 2.18.9, 2.22.1 | com.fasterxml.jackson.core/jackson-databind: Jackson-databind: Privilege escalation via improper handling of @JsonUnwrapped properties |
| MEDIUM | CVE-2026-77310 | com.fasterxml.jackson.core:jackson-databind | 2.21.1 | 2.18.9, 2.21.5, 2.22.1 | com.fasterxml.jackson.core/jackson-databind: jackson-databind: Server-Side Request Forgery and internal host enumeration via eager DNS resolution |
| MEDIUM | CVE-2026-83557 | com.fasterxml.jackson.core:jackson-databind | 2.21.1 | 2.18.10, 2.21.6, 2.22.2 | com.fasterxml.jackson.core/jackson-databind: tools.jackson.core/jackson-databind: jackson-databind: Path traversal via incomplete type validation |
| MEDIUM | GHSA-mhm7-754m-9p8w | com.fasterxml.jackson.core:jackson-databind | 2.21.1 | 2.18.9, 2.21.5 | jackson-databind: `@JsonView` bypass for creator properties with `@JsonTypeInfo(include=As.EXTERNAL_PROPERTY)` |
| MEDIUM | CVE-2024-6763 | org.eclipse.jetty:jetty-http | 9.4.54.v20240208 | 12.0.12 | org.eclipse.jetty:jetty-http: jetty: Jetty URI parsing of invalid authority |
| LOW | CVE-2026-10532 | ch.qos.logback:logback-core | 1.5.32 | 1.5.34 | Deserialization of untrusted data vulnerability in QOS.CH Sarl logback ... |
| LOW | CVE-2026-9828 | ch.qos.logback:logback-core | 1.5.32 | 1.5.33 | Deserialization of untrusted data vulnerability in QOS.CH Sarl logback ... |
| LOW | CVE-2025-11143 | org.eclipse.jetty:jetty-http | 9.4.54.v20240208 | 12.0.31, 12.1.5 | org.eclipse.jetty/jetty-http: org.eclipse.jetty: Security bypass due to differential URI parsing |
Previous scans
Daily Trivy refresh. Current report plus the last 14 full scans; older copies are deleted.
| Scanned | Vuln DB | Version | Wrap | Vendor | Report |
|---|---|---|---|---|---|
| 2026-10-14 06:50 UTC | 2026-10-14 | 2.5.5 | none | 9 HIGH · 12 MEDIUM · 3 LOW | JSON |
| 2026-10-13 06:56 UTC | 2026-10-13 | 2.5.5 | none | 9 HIGH · 12 MEDIUM · 3 LOW | JSON |
| 2026-10-12 09:27 UTC | 2026-10-12 | 2.5.5 | none | 9 HIGH · 12 MEDIUM · 3 LOW | JSON |
| 2026-10-12 06:50 UTC | 2026-10-12 | 2.5.5 | none | 9 HIGH · 12 MEDIUM · 3 LOW | JSON |
| 2026-10-11 06:51 UTC | 2026-10-11 | 2.5.5 | none | 9 HIGH · 12 MEDIUM · 3 LOW | JSON |
| 2026-10-10 06:51 UTC | 2026-10-10 | 2.5.5 | none | 9 HIGH · 12 MEDIUM · 3 LOW | JSON |
| 2026-10-09 06:50 UTC | 2026-10-08 | 2.5.5 | none | 9 HIGH · 12 MEDIUM · 3 LOW | JSON |
| 2026-10-08 19:31 UTC | 2026-10-08 | 2.5.5 | none | 9 HIGH · 12 MEDIUM · 3 LOW | JSON |
| 2026-10-08 06:50 UTC | 2026-10-07 | 2.5.5 | none | 9 HIGH · 12 MEDIUM · 3 LOW | JSON |
| 2026-10-07 06:51 UTC | 2026-10-07 | 2.5.5 | none | 9 HIGH · 12 MEDIUM · 3 LOW | JSON |
| 2026-10-06 06:51 UTC | 2026-10-06 | 2.5.5 | none | 9 HIGH · 12 MEDIUM · 3 LOW | JSON |
| 2026-09-27 07:33 UTC | 2026-09-27 | 2.5.5 | none | 4 HIGH · 9 MEDIUM · 3 LOW | JSON |
| 2026-09-27 06:52 UTC | 2026-09-27 | 2.5.5 | none | 4 HIGH · 9 MEDIUM · 3 LOW | JSON |
| 2026-09-26 07:07 UTC | 2026-09-26 | 2.5.5 | none | 4 HIGH · 9 MEDIUM · 3 LOW | JSON |