Wasabi Wallet
Privacy-focused Bitcoin wallet
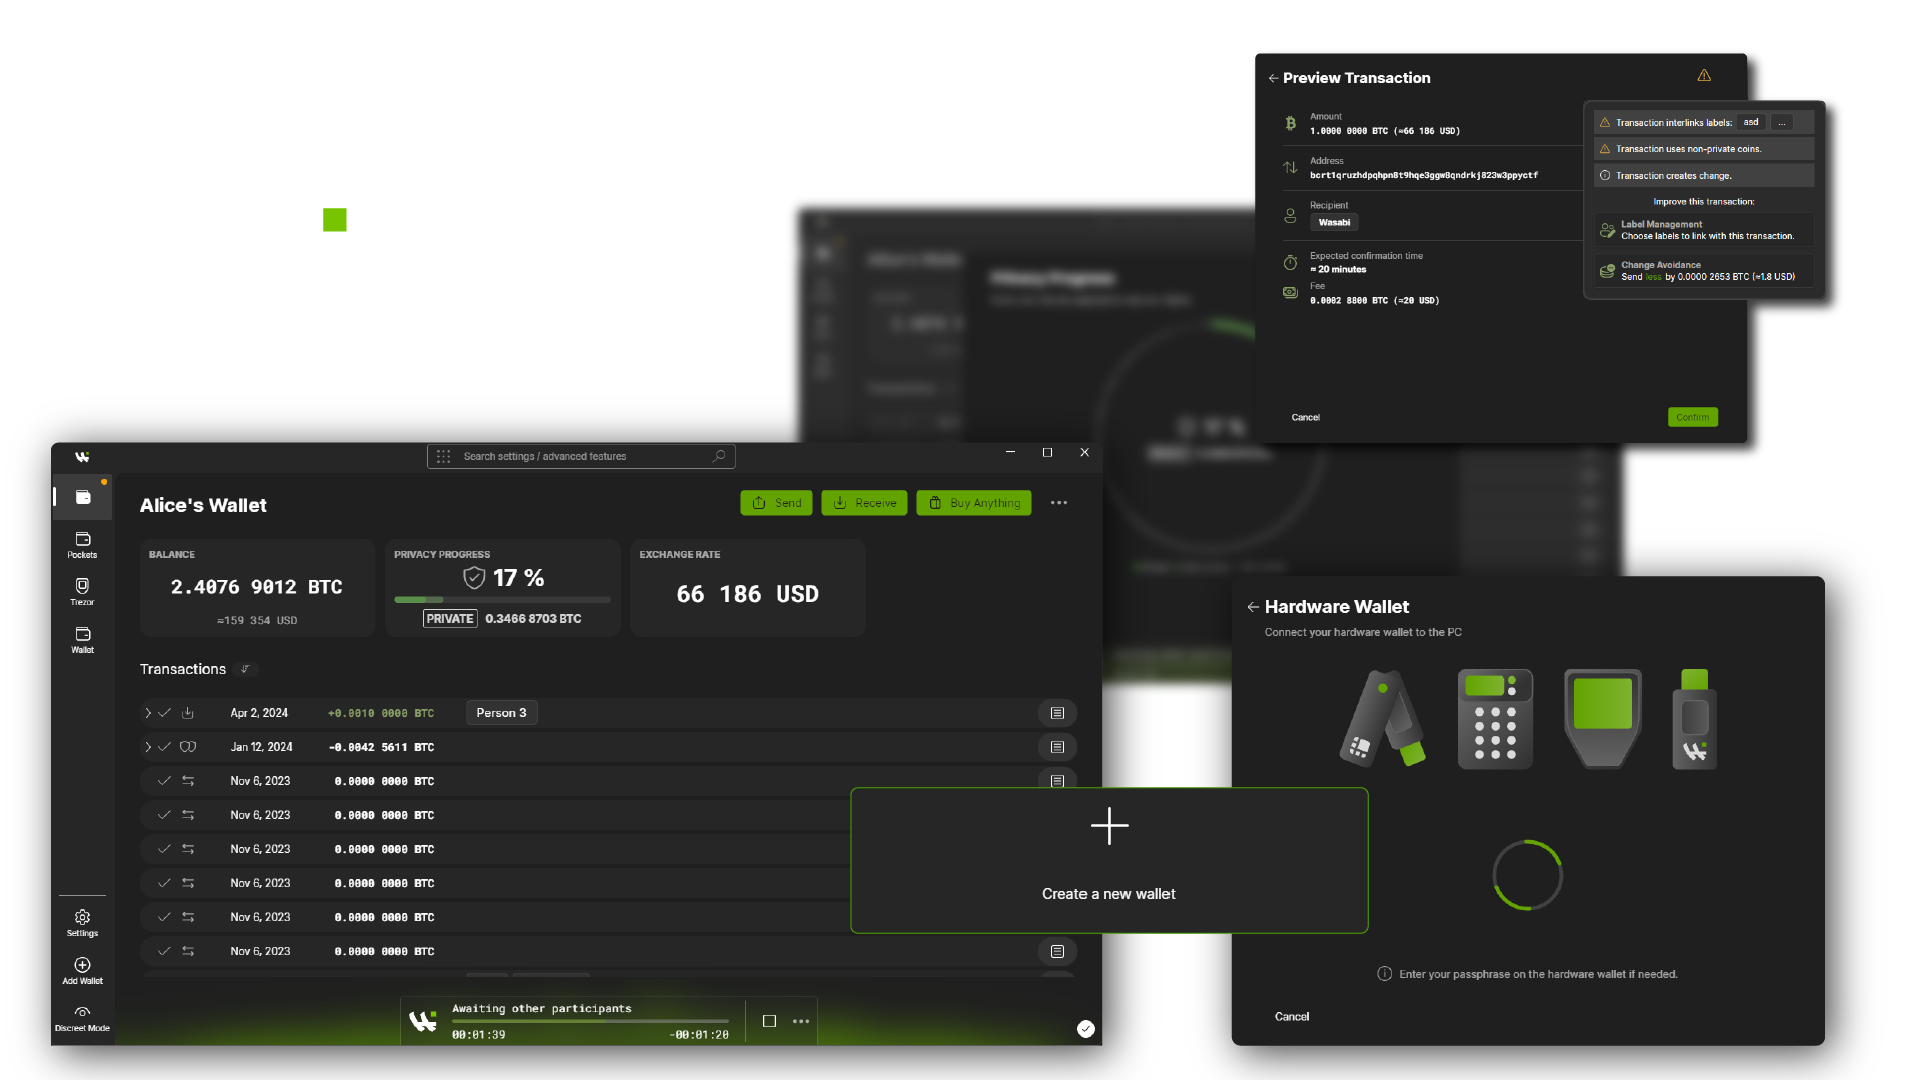
Wasabi Wallet. This Flatpak will wrap the official Linux package. It is not a vendor-official Flatpak.
Wasabi is MIT; this Flatpak is a redistribution, not vendor official.
Install
flatpak --user remote-add --if-not-exists thepeoples \
  https://flatpak.thepeoples.io/thepeoples.flatpakrepo
flatpak --user install -y thepeoples io.thepeoples.Wasabi
flatpak --user install -y thepeoples io.thepeoples.Wasabi//2.8.4
Optional system install uses sudo flatpak remote-add --if-not-exists --system and sudo flatpak install -y --system. The //version form pins the advertised ostree branch; stable tracks the latest advertised tree.
Previous versions
The remote keeps the current tree plus the last two vendor versions as extra ostree branches for rollback. Objects stay on the remote after a branch is dropped (publish does not delete).
- Version
2.8.1(ostree7735e2934bfc78c83bdee8fadbc3e76f03f86ee37424d8934c33c89330bf81be)
flatpak --user install -y thepeoples io.thepeoples.Wasabi//2.8.1- Version
2.8.2(ostree38c923b9d3868bb49c6bbb88788b00e7bd48e50aa8205ea2ba105273a2a36135)
flatpak --user install -y thepeoples io.thepeoples.Wasabi//2.8.2Verify
- App id
io.thepeoples.Wasabi, vendor zkSNACKs, version2.8.4, license MIT - Download 97.9 MB · installed 216.0 MB
- sha256
c7befcea3d17e3c59ac16d00b5c9e8eeb04177e35c13069b8d2c943710058698 - Ostree key fingerprint
98D786877B6C4E8C6889CBD2E75B1C5B0CB2D841 - Vendor key fingerprint
6FB3872B5D42292F59920797856348328949861E - Homepage https://wasabiwallet.io/
Input scan
Pinned tarball Wasabi-2.8.4-linux-x64.tar.gz, extracted without install scripts, scanned before wrap. 2026-10-14 19:38 UTC · trivy 0.73.0 · vuln DB 2026-10-14.
Wrap
Layers this remote adds. Gate fails on CRITICAL.
none
gate pass
Vendor
In the upstream package. Not patched here.
2 CRITICAL · 10 HIGH · 2 MEDIUM
Vendor findings 14 · 2 CRITICAL · 10 HIGH · 2 MEDIUM
| Severity | ID | Package | Installed | Fixed | Title |
|---|---|---|---|---|---|
| CRITICAL | CVE-2026-70188 | Microsoft.AspNetCore.App.Runtime.linux-x64 | 10.0.12 | 11.0.0-rc.2, 8.0.32, 10.0.13, 9.0.21 | Microsoft Security Advisory CVE-2026-70188 - ASP.NET Core Security Feature Bypass Vulnerability |
| CRITICAL | CVE-2026-88092 | Microsoft.AspNetCore.App.Runtime.linux-x64 | 10.0.12 | 8.0.32, 10.0.13, 11.0.0-rc.2, 9.0.21 | Microsoft Security Advisory CVE-2026-88092 - ASP.NET Core Security Feature Bypass Vulnerability |
| HIGH | CVE-2026-70175 | Microsoft.AspNetCore.App.Runtime.linux-x64 | 10.0.12 | 9.0.21, 10.0.13, 8.0.32 | Microsoft Security Advisory CVE-2026-70175 - ASP.NET Core Elevation of Privilege Vulnerability |
| HIGH | CVE-2026-70181 | Microsoft.AspNetCore.App.Runtime.linux-x64 | 10.0.12 | 9.0.21, 10.0.13, 8.0.32 | Microsoft Security Advisory CVE-2026-70181 - ASP.NET Core Denial of Service Vulnerability |
| HIGH | CVE-2026-70183 | Microsoft.AspNetCore.App.Runtime.linux-x64 | 10.0.12 | 8.0.32, 10.0.13, 9.0.21, 11.0.0-rc.2 | Microsoft Security Advisory CVE-2026-70183 - ASP.NET Core Security Feature Bypass Vulnerability |
| HIGH | CVE-2026-70186 | Microsoft.AspNetCore.App.Runtime.linux-x64 | 10.0.12 | 8.0.32, 10.0.13, 9.0.21 | Microsoft Security Advisory CVE-2026-70186 - ASP.NET Core Denial of Service Vulnerability |
| HIGH | CVE-2026-96236 | Microsoft.AspNetCore.App.Runtime.linux-x64 | 10.0.12 | 8.0.32, 11.0.0-rc.2, 10.0.13, 9.0.21 | Microsoft Security Advisory CVE-2026-96236 - ASP.NET Core Denial of Service Vulnerability |
| HIGH | CVE-2026-58280 | Microsoft.NETCore.App.Runtime.linux-x64 | 10.0.12 | 9.0.21, 8.0.32, 10.0.13, 11.0.0-rc.2 | Microsoft Security Advisory CVE-2026-58280 - .NET and Visual Studio Denial of Service Vulnerability |
| HIGH | CVE-2026-69651 | Microsoft.NETCore.App.Runtime.linux-x64 | 10.0.12 | 9.0.21, 11.0.0-rc.2, 10.0.13, 8.0.32 | Microsoft Security Advisory CVE-2026-69651 - .NET and Visual Studio Denial of Service Vulnerability |
| HIGH | CVE-2026-96225 | Microsoft.NETCore.App.Runtime.linux-x64 | 10.0.12 | 8.0.32, 10.0.13, 11.0.0-rc.2, 9.0.21 | Microsoft Security Advisory CVE-2026-96225 - .NET and Visual Studio Elevation of Privilege Vulnerability |
| HIGH | CVE-2026-96231 | Microsoft.NETCore.App.Runtime.linux-x64 | 10.0.12 | 8.0.32, 10.0.13, 9.0.21, 11.0.0-rc.2 | Microsoft Security Advisory CVE-2026-96231 - .NET and Visual Studio Elevation of Privilege Vulnerability |
| HIGH | CVE-2026-96233 | Microsoft.NETCore.App.Runtime.linux-x64 | 10.0.12 | 10.0.13, 11.0.0-rc.2, 9.0.21, 8.0.32 | Microsoft Security Advisory CVE-2026-96233 - .NET and Visual Studio Denial of Service Vulnerability |
| MEDIUM | CVE-2026-70196 | Microsoft.AspNetCore.App.Runtime.linux-x64 | 10.0.12 | 8.0.32, 10.0.13, 9.0.21 | Microsoft Security Advisory CVE-2026-70196 - ASP.NET Core Denial of Service Vulnerability |
| MEDIUM | CVE-2026-66822 | Microsoft.NETCore.App.Runtime.linux-x64 | 10.0.12 | 9.0.21, 11.0.0-rc.2, 10.0.13, 8.0.32 | Microsoft Security Advisory CVE-2026-66822 - .NET and Visual Studio Information Disclosure Vulnerability |
Previous scans
Daily Trivy refresh. Current report plus the last 14 full scans; older copies are deleted.
| Scanned | Vuln DB | Version | Wrap | Vendor | Report |
|---|---|---|---|---|---|
| 2026-10-14 06:51 UTC | 2026-10-14 | 2.8.3 | none | 2 CRITICAL · 10 HIGH · 2 MEDIUM | JSON |
| 2026-10-13 06:57 UTC | 2026-10-13 | 2.8.3 | none | none | JSON |
| 2026-10-12 09:28 UTC | 2026-10-12 | 2.8.3 | none | none | JSON |
| 2026-10-12 06:51 UTC | 2026-10-12 | 2.8.3 | none | none | JSON |
| 2026-10-11 06:52 UTC | 2026-10-11 | 2.8.3 | none | none | JSON |
| 2026-10-10 06:51 UTC | 2026-10-10 | 2.8.3 | none | none | JSON |
| 2026-10-09 06:51 UTC | 2026-10-08 | 2.8.3 | none | none | JSON |
| 2026-10-08 19:31 UTC | 2026-10-08 | 2.8.3 | none | none | JSON |
| 2026-10-08 06:51 UTC | 2026-10-07 | 2.8.3 | none | none | JSON |
| 2026-10-07 06:51 UTC | 2026-10-07 | 2.8.3 | none | none | JSON |
| 2026-10-06 06:51 UTC | 2026-10-06 | 2.8.3 | none | none | JSON |
| 2026-09-27 07:34 UTC | 2026-09-27 | 2.8.3 | none | none | JSON |
| 2026-09-27 06:52 UTC | 2026-09-27 | 2.8.3 | none | none | JSON |
| 2026-09-26 07:08 UTC | 2026-09-26 | 2.8.3 | none | none | JSON |